CHAPTER 3 – SECURITY THROUGH AUTHENTICATION AND ENCRYPTION
TRUE/FALSE
1. Sniffer software turns the NIC on its host computer into a virtual listening ear, capturing the network
traffic that goes across that NIC on a particular network segment.
2. The ethereal sniffer software only functions on Linux/UNIX computers.
3. In stream cipher, a specific key size is used for encryption.
4. A secret key is used to both encrypt and decrypt data.
5. The public key/private key method uses an encryption algorithm developed by Joan Daemen and
Vincent Rijmen.
6. The original version of DES used a 56-bit encryption key combined with 8-bit parity.
7. Triple DES is a standard adopted by the U.S. government to replace AES.
8. The purpose of EFS is to protect folder and file contents on a hard disk, in case a hard disk is stolen
from a server or workstation, or a portable computer is lost or stolen.
9. CFS can be used for remote file access through the NFS used by Netware systems.
10. Session authentication works by giving each frame or packet an identification or sequence number.
MODIFIED TRUE/FALSE
1. A random generator starts with a base or seed number and generates the same sequence of random
numbers time after time. _________________________
2. When a network consists of Windows 2000 or later operating systems, Kerberos is the preferred logon
authentication method. _________________________
3. Today, Kerberos is the most commonly used form of security for communications and transactions
over the Web. _________________________
4. TLS uses private-key symmetric data encryption and the TLS Handshake Protocol for secure
communications. _________________________
5. When an SSL communication session begins between two computers, the computers first exchange
certificates to authenticate the receiver and sender. _________________________
6. In TCP/IP communications using IPv4, the authentication header is placed after the traditional IP
header field in a packet and before the TCP (or UDP) field. _________________________
7. Authentication makes data unintelligible to everyone except its intended recipients.
_________________________
8. Secret key encryption uses a public key and a private key. _________________________
9. When the hashing method of encryption is used, each password has a unique digital signature.
_________________________
10. Message Digest 4 takes the original data and adds padded spaces until the length of the data section is
456 bytes. _________________________
MULTIPLE CHOICE
1. _____ is the use of a secret code or other means to disguise data that is stored on a computer or
transported across a network.
a.
Encryption
c.
Hashing
b.
Authentication
d.
Ciphering
2. Which of the following sniffer application can be used in Windows-based operating systems?
a.
The Sniffer
d.
Both a and b
b.
windump
e.
a, b, and c
c.
Sniffit
3. What encryption method is often used to create a digital signature?
a.
Secret key
c.
DES
b.
Hashing
d.
CFS
4. Which version of hashing algorithm takes 8-bit (one-byte) chunks and creates an encrypted message
that is padded until its length can be divided by 16?
a.
MD2
c.
MD5
b.
MD4
d.
SHA-1
5. Which version of hashing algorithm uses a mathematical formula to reduce a message to 160 bits and
then hashes a digital signature to go with the message?
a.
MD2
c.
MD5
b.
MD4
d.
SHA-1
6. When was the RSA encryption method created?
a.
1967
c.
1987
b.
1977
d.
1997
7. Which of the following encryption algorithms is considered to be the most secure?
a.
MD5
c.
RSA
b.
DES
d.
3DES
8. What encryption method does Red Hat Linux use by default?
a.
RSA
c.
DES3
b.
DES
d.
PAM
9. What type of encryption is used for remote connections into Windows 2000 Server and Windows
Server 2003?
a.
DES
c.
PPTP
b.
PPP
d.
MPPE
10. What is the RSA key size used by MPPE when it is configured for strongest encryption?
a.
40 bits
c.
128 bits
b.
54 bits
d.
254 bits
11. What command can be used from the command prompt window to configure EFS?
a.
hash
c.
msconfig
b.
efsconfig
d.
cipher
12. Which of the following cipher command-line parameters decrypts the contents of the specified folder
and sets the folder so that any files added to the folder are not encrypted?
a.
/?
c.
/d
b.
/e
d.
/n
13. Which of the following cipher command-line parameters provides the account employing cipher with a
new encryption key?
a.
/n
c.
/k
b.
/u
d.
/x
14. Which of the following cipher command-line parameters copies encryption key and certificate data to
a file that is encrypted for use by the cipher user?
a.
/?
c.
/e
b.
/k
d.
/x
15. Which of the following encryption techniques is employed in UNIX/Linux systems to enable
encryption in file systems, using DES, 3DES, and other encryption techniques?
a.
RSA
c.
CFS
b.
PAM
d.
AES
16. _____ authentication works by giving each frame or packet an identification or sequence number. This
ensures the accuracy of ongoing communications and the authenticity of the communications source.
a.
Network
c.
System
b.
Session
d.
Frame
17. When following the ISO _____ format, a digital certificate includes a basic set of encrypted
information.
a.
X10
c.
X.509
b.
X.502
d.
X 802.3
18. Which of the following operating systems recognizes the original NTLM logon authentication?
a.
Windows 3.11
d.
Both a and b
b.
Windows 95
e.
a, b, and c
c.
Windows Server 2003
19. What needs to be installed in order for Windows 95 and Windows 98 to use NTLM v2?
a.
Service pack 1
c.
NTLM v2 client install
b.
Directory Service Client
d.
Nothing
20. _____ is an authenticating server for EAP.
a.
IAS
c.
ISA
b.
IIS
d.
RADIUS
21. What size of keys can be used with SSL authentication?
a.
40 bit only
c.
40 bit, 56 bit, and 128 bit
b.
40 bit and 128 bit
d.
40 bit and 56 bit
22. What authentication method was designed using SSL as a model and is supported by the IETF as an
Internet standard for secure communications?
a.
EAP
c.
TLS
b.
SSL+
d.
IPSec
23. What does SSH use to authenticate a communications session that uses passwords?
a.
Digital certificates
d.
Both a and b
b.
RSA
e.
Both a and c
c.
EAP
24. Why is SSH particularly suited to UNIX/Linux systems?
a.
It uses native code
c.
It is based on the UNIX kernel
b.
It uses pipes
d.
None of the above
25. Which authentication method authenticates by using tickets to verify client and server
communications, and employs private-key encryption?
a.
Digital certificates
c.
Kerberos
b.
Secure Sockets Layer
d.
Security Token
26. Which authentication method is used on networks and in remote communications, typically employing
Remote Authentication Dial-in User Servers and is compatible with many encryption methods?
a.
SSL
c.
EAP
b.
Kerberos
d.
TLS
27. Which authentication method is a physical device that enables the generation of a unique password
each time a user logs on to a server or network?
a.
SSH
c.
Digital certificate
b.
Security token
d.
Session
28. Which authentication method employs a unique set of digital information or a digital signature with a
communication or a file as a means to verify the source and uses public-key asymmetrical encryption?
a.
SSL
c.
Digital certificates
b.
TLS
d.
Kerberos
29. Which authentication method is used in Internet and network communications, and employs a
handshaking protocol for authentication plus RSA for encryption?
a.
EAP
c.
SSH
b.
TLS
d.
SSL
30. _____ is a set of IP-based secure communications and encryption standards created by the IETF, and
was developed to provide secure network communications.
a.
SSL
c.
PPTP
b.
IPSec
d.
LDAP
31. At what TCP/IP layer does IPSec secure communications?
a.
Transport
c.
Network
b.
Application
d.
Physical
32. With which version(s) of IP is IPSec compatible?
a.
IPv4
d.
Both a and c
b.
IPv5
e.
Both a and b
c.
IPv6
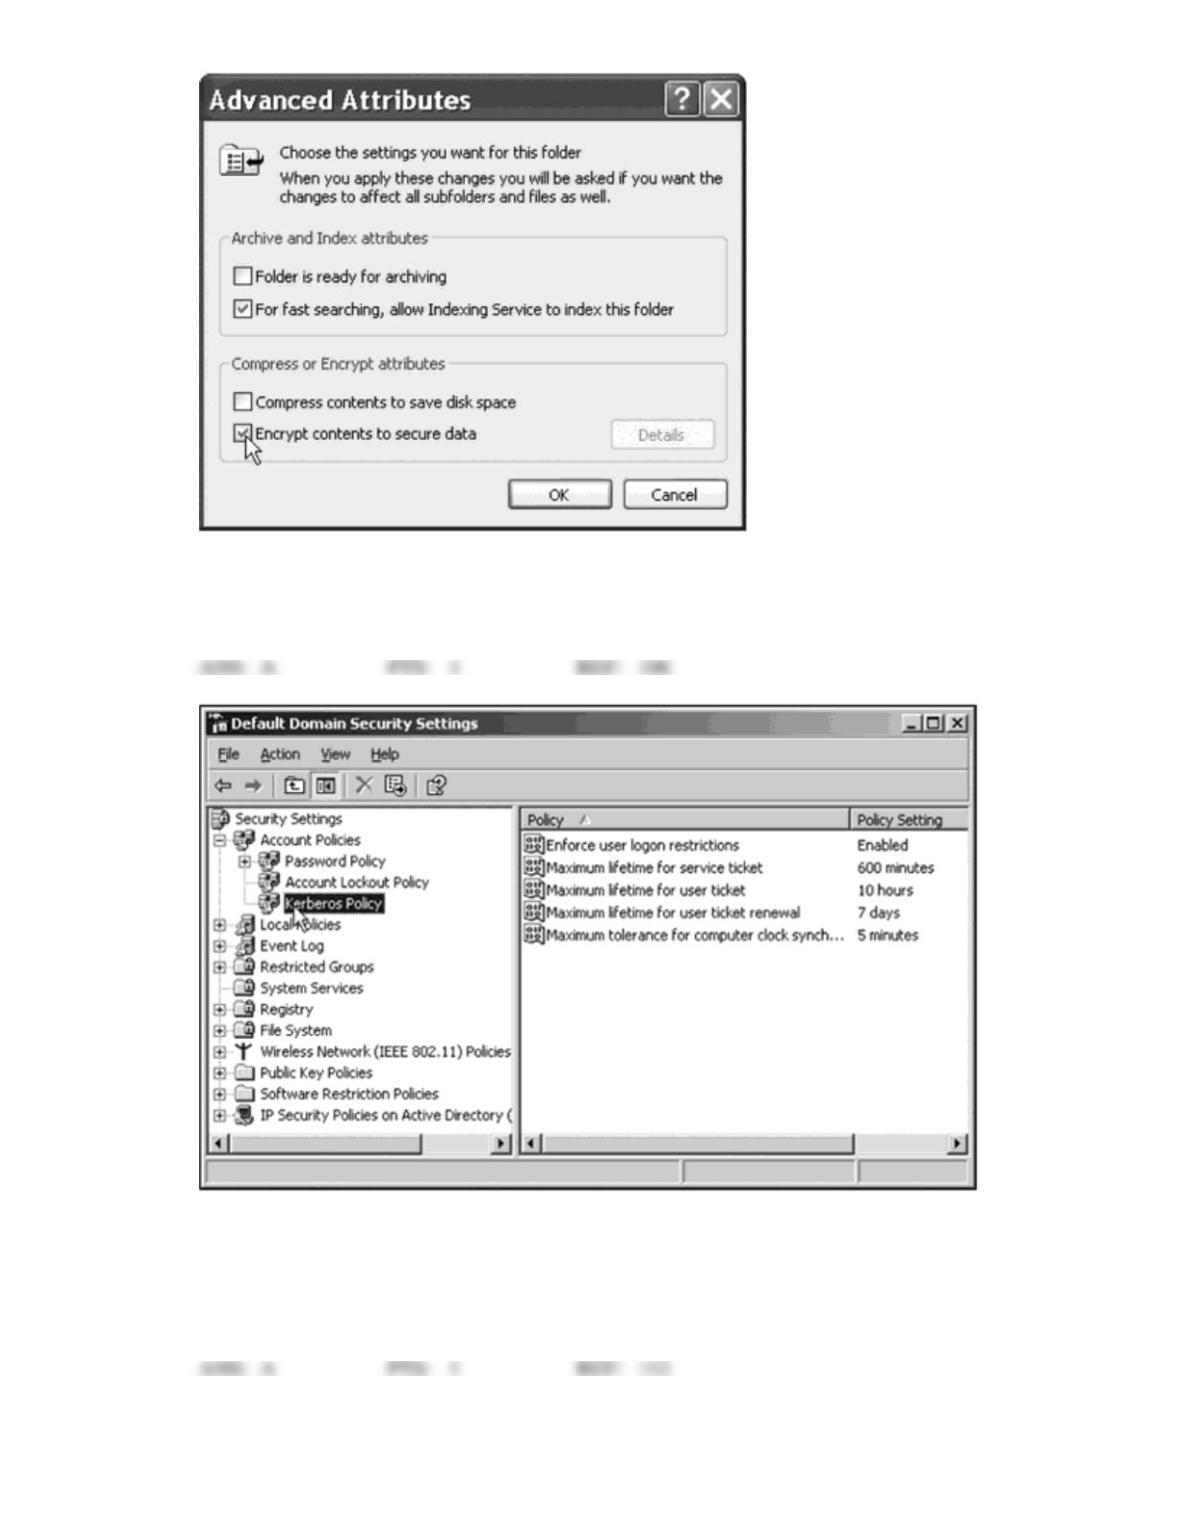
33. What form of encryption is being enabled in the figure above?
a.
EFS
c.
DES
b.
MPPE
d.
CFS
34. Which option in the figure above turns Kerberos encryption on and off?
a.
Enforce user logon restrictions
b.
Maximum lifetime for a service ticket
c.
Maximum lifetime for user ticket renewal
d.
Maximum tolerance for computer clock synchronization
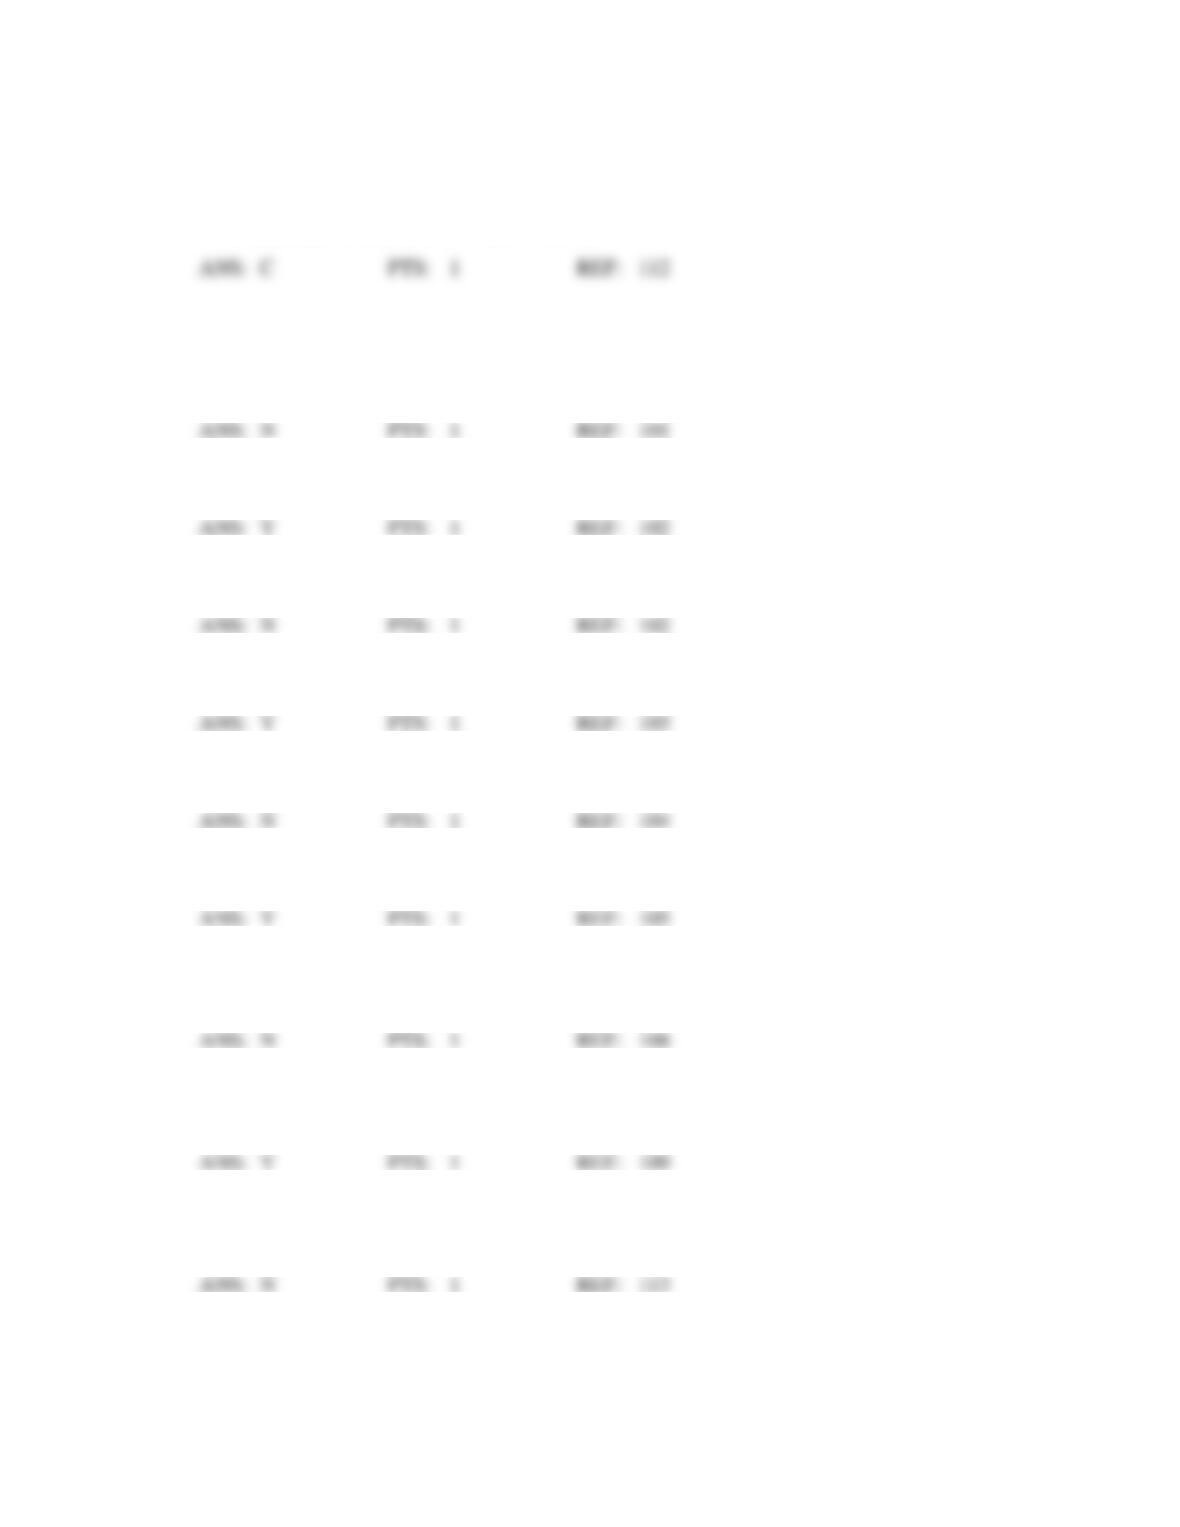
35. If getting users to log off when they go home at night is a problem, which option should you modify in
the figure above?
a.
Enforce user logon restrictions
b.
Maximum lifetime for a service ticket
c.
Maximum lifetime for a user ticket
d.
Maximum lifetime for user ticket renewal
YES/NO
1. Is MD4 incorporated into Microsoft’s MS-CHAP v2 hashing algorithm?
2. Did the original version of DES use a 56-bit encryption key combined with 8-bit parity?
3. Are user passwords in Red Hat Linux encrypted using 3DES and stored in the /etc/passwd file?
4. Is the maximum size of the private key in AES 256 bits in length?
5. Was AES originally developed for the U.S. National Security Agency?
6. Does Microsoft’s MPPE use a 40-bit RSA encryption key for its basic encryption?
7. Does the Encrypting File System (EFS) employ public- and private-key asymmetrical encryption and a
trapdoor function to manipulate prime numbers?
8. In session authentication, is each packet given a sequence number when it is constructed at the source
computer?
9. Was SSH developed by Netscape to provide authentication security for TCP/IP applications such as
FTP and Telnet?
10. Does each security token have a unique identification number built into it, so that the authentication
server can verify the security token before issuing a password?
COMPLETION
1. ____________________ authenticates by using tickets to verify client and server communications,
and employs private-key encryption.
2. ____________________ authentication method is an application-independent form of authentication
that is modeled after SSL and uses RSA encryption.
3. When Windows 2000 Server or Windows Server 2003 is contacted by a client using IPSec configured
in the Client (____________________) role, it will respond by using IPSec communication.
4. The ____________________ field in the AH uses a special counter to activate anti-replay so that the
receiver can determine if it has already received a packet.
5. The ____________________ field in the ESP is used in the same way as in the AH, to store the
Integrity Check Value.
6. Deploying _________________________ with NAT can interfere with the security established by
IPSec.
7. In a(n) ____________________ attack every character combination is used in an attempt to determine
the password of an account.
8. ____________________ is the science of creating secret messages.
9. The DES, AES, and MPPE encryption methods are all forms of the ____________________
encryption method, but use different block sizes, key sizes, and algorithms.
10. ____________________ encryption can work well on a computer for files that are only accessed by an
authorized account, but it is difficult to achieve secrecy over a network using this method.
MATCHING
Match the following terms to the appropriate definitions.
a.
AES
f.
NTLM
b.
CFS
g.
PAM
c.
EFS
h.
PPP
d.
EAP
i.
PPTP
e.
MPPE
j.
SSH
1. A multipurpose authentication method
2. A module that can be installed in Linux without rewriting existing system code
3. Adopted by the U.S. government to replace DES and 3DES
4. Communications protocol that supports TCP/IP, NetBEUI, and IPX/SPX
5. Used by Microsoft for remote communications over PPP or PPTP
6. Communications protocol that enables Internet connections to VPNs
7. Enables Linux and UNIX disk file systems and NFS files to be encrypted
8. Authentication developed for UNIX/Linux to provide authentication security
9. Logon authentication compatible with all Windows operating systems
10. Enables a user to encrypt the contents of a folder or a file
8. ANS: J PTS: 1 REF: 124
9. ANS: F PTS: 1 REF: 123
10. ANS: C PTS: 1 REF: 122
SHORT ANSWER
1. List eight different encryption techniques that are designed to help protect stored or transmitted data.
2. List the four hashing algorithms typically used.
3. List and provide the key lengths for the three different flavors of RSA used by MPPE.
4. List six of the common authentication methods in use today.
5. When following the ISO X.509 format, what basic set of encrypted information does a digital
certificate include?
6. List six applications that can be used with SSL.
7. In Windows 2000 and Windows 2003, a computer that is configured to use IPSec communication can
function in three roles. What are they?
8. List the six specific fields in the AH.
9. Which seven specific fields are contained in the ESP?
10. List five common types of attacks on encryption and authentication.