CHAPTER 12 – SECURITY THROUGH MONITORING AND AUDITING
TRUE/FALSE
1. Active intrusion detection is effective as long as the server or network administrator regularly checks
the logs and recorded information for possible intrusion attempts.
2. At minimum, active intrusion detection alerts a server or network administrator about an attack or
intrusion, so the administrator can take action.
3. Network-based intrusion-detection software is categorized as host wrappers or host-based agents.
4. An inspector is an IDS that tracks a full range of data and events related to an operating system or
network.
5. The device log records information about system-related events such as hardware errors, driver
problems, and hard drive errors.
6. In Windows Server 2003 event viewer, an informational message such as a notice that a service has
been started is prefaced by a black “!” (exclamation point) that appears on a yellow caution symbol.
7. In Red Hat Linux 9.x, by default, each log file has four rotation levels, to enable the retention of up to
four weeks of information.
8. The Netware 6.x Console Log enables you to trace information, such as NLMs that have been loaded
or unloaded, and to trace other activities that have been performed from the console.
9. In Mac OS X, the FTP Log keeps track of file uploads, downloads, and communications with FTP
servers.
10. In Red Hat Linux, the Emacs and vi editors can be used to configure the syslog.conf file.
MODIFIED TRUE/FALSE
1. File locks are open communication links between two processes on the server or between the server
and a client. _________________________
2. The who command provides information about who is logged on to Red Hat Linux 9.x.
_________________________
3. SYSCON is a Server Console command that is carried forward from earlier versions of NetWare.
_________________________
4. Network Monitor is a utility which comes with Windows 2000 Server and Windows Server 2003.
_________________________
5. The default folder for saved Network Monitor capture information in Windows Server 2003 is
\WINNT\system32\NETMON\CAPTURES. _________________________
6. Network Monitor supports event management, which enables a server administrator to set up filters to
capture a certain event or type of network activity. _________________________
7. In Network Monitor the capture store is the amount of RAM and virtual memory that is used to store
captured data. _________________________
8. If % Network utilization is frequently over 90 percent, that means the network is experiencing
collisions and there may be bottlenecks due to the network design, possibly indicating the need to
create more or different subnets. _________________________
9. Understanding the normal conditions for operating systems and a network is accomplished by
establishing baselines. _________________________
10. SNMP enables network agents to gather information about network performance and send that
information to a network management station. _________________________
MULTIPLE CHOICE
1. Gathering performance statistics each time a new software application is installed, on slow, average,
and peak periods during its use, and tracking how many users are on that software is an example of
acquiring a _____.
a.
baseline
c.
foundation
b.
framework
d.
utilization level
2. Which of the following options is a common approach to intrusion detection?
a.
Archive
d.
Both a and b
b.
System-based
e.
Both b and c
c.
Host-based
3. Which of the following activities are usually looked for using passive intrusion-detection tools?
a.
Unusual or excessive e-mail traffic
d.
Port scans
b.
Changes to security
e.
All of the above
c.
Unplanned system shutdowns
4. Which of the following are examples of active intrusion-detection tools?
a.
klaxon
c.
AppShield
b.
lsof
d.
RealSecure
5. Which passive intrusion-detection tool provides a listing of open files, including suspicious open files?
a.
klaxon
c.
Dragon Squire
b.
lsof
d.
PreCis
6. Which passive intrusion-detection tool monitors network activity and includes a proprietary
programming language to customize the way it captures and analyzes information?
a.
klaxon
c.
Dragon Squire
b.
Real Secure
d.
Network Flight Recorder
7. Which passive intrusion-detection tool audits activities on multiple operating systems, filters them, and
collects the information into one large database for analysis of intrusions?
a.
loginlog
c.
PreCis
b.
lsof
d.
RealSecure
8. Which active intrusion-detection tool monitors HTML activity and blocks attacks?
a.
Entercept
c.
Snort
b.
AppShield
d.
StormWatch
9. Which active intrusion-detection tool monitors for intruders and can take action on the basis of
preestablished security policies?
a.
Entercept
c.
SecureHost
b.
Symantec Intruder Alert
d.
Storm Watch
10. Which active intrusion-detection tool is a distributed system that works on servers and clients and
denies application requests that are not permitted, on the basis of a security policy applying to the
servers and clients?
a.
Entercept
c.
SecureHost
b.
AppShield
d.
Storm Watch
11. What type of intrusion detection monitors the system on which it is loaded?
a.
Host-based
c.
Network-based
b.
System-based
d.
Local-based
12. Which of the following network activities may be monitored by a personal firewall?
a.
Remote logon attempts
d.
All of the above
b.
Port scanning
e.
None of the above
c.
Dial-in attempts
13. Which type of intrusion detection focuses on monitoring network traffic associated with a specific
network segment?
a.
Host-based
c.
Network-based
b.
System-based
d.
LAN-based
14. Which type of IDS looks for excessive use of a computer’s resources, such as the CPU or memory?
a.
Passive
c.
Inspector
b.
Network-based
d.
Auditor
15. Which type of intrusion detection system looks for intrusion signatures on ports, through frame and
packet headers, and through commands?
a.
Network-based
c.
Auditor
b.
Host-based
d.
Inspector
16. Which type of IDS automatically records information to a log?
a.
Network-based
c.
Auditor
b.
Host-based
d.
Inspector
17. What type of computer is placed on a network to attract attackers?
a.
Dummy
d.
Both a and b
b.
Honeypot
e.
Both b and c
c.
Fake
18. What are the three principle event logs in Windows 2000 Server and Windows Server 2003?
a.
System, Security, Application
b.
System, Security, Directory Service
c.
System, Directory Service, DNS
d.
Security, Directory Service, Application
19. Which event log records events that are associated with Active Directory?
a.
Active Directory
c.
System
b.
Directory Service
d.
None of the above
20. In the event log, what type of event is indicated with a white “x” that appears inside a red circle?
a.
Information
c.
Standby
b.
Warning
d.
Error
21. In the event log, a notice that a service has started would be indicated with what type of symbol?
a.
A blue “i” displayed in a white comment bubble
b.
A black “!” that appears on a yellow caution symbol
c.
A white “x” that appears inside a red circle
d.
A red “x” that appears inside a white circle
22. In event log, a warning that a CD-ROM is not loaded would be indicated by what type of symbol?
a.
A blue “i” displayed in a white comment bubble
b.
A black “!” that appears on a yellow caution symbol
c.
A white “x” that appears inside a red circle
d.
A red “x” that appears inside a white circle
23. By default in Red Hat Linux 9.x , how many rotation levels does each log file have?
a.
2
c.
4
b.
3
d.
5
24. What directory are the default logs kept in Red Hat Linux 9.x?
a.
/etc/log
c.
/bin/log
b.
/var/log
d.
/conf/log
25. In Netware, in which directory are the Access log and the Error log kept?
a.
SYS:NOVONYX\SUITESPOT\ADMIN-SERV\LOGS\
b.
SYS:ETC\
c.
SYS:VAR\
d.
SYS:NOVONYX\SUITESPOT\LOGS\
26. In Netware 6.x, what directory contains the Audit log and the Console log?
a.
SYS:NOVONYX\SUITESPOT\ADMIN-SERV\LOGS\
b.
SYS:ETC\
c.
SYS:VAR\
d.
SYS:NOVONYX\SUITESPOT\LOGS\
27. In Mac OS X, which log contains information about printing activities?
a.
/var/log/lookupd.log
c.
/var/log/secure.log
b.
/var/log/lpr.log
d.
/var/log/system.log
28. What utility can be used to clean up the Mac OS X Server logs?
a.
MacJanitor
c.
MacSweep
b.
MacCleanUp
d.
MacRotate
29. Which command provides information about who is logged on to Red Hat Linux 9.x?
a.
who
c.
proc
b.
who am i
d.
login
30. Which Linux Red Hat 9.x “who” command option shows the amount of time each user process has
been idle?
a.
-a
c.
-i
b.
-b
d.
-s
31. Which Network Monitor pane provides statistics about traffic from other computers on the network,
including the MAC (device) address of each computer’s NIC and data about the number of frames sent
from and received by each computer?
a.
Graph
c.
Session Statistics
b.
Total Statistics
d.
Station Statistics
32. Which Network Monitor statistic shows total traffic in frames for broadcasts, unicasts, and multicasts?
a.
% Network Utilization
c.
Broadcasts Per Second
b.
Frames Per Second
d.
Muticasts Per Second
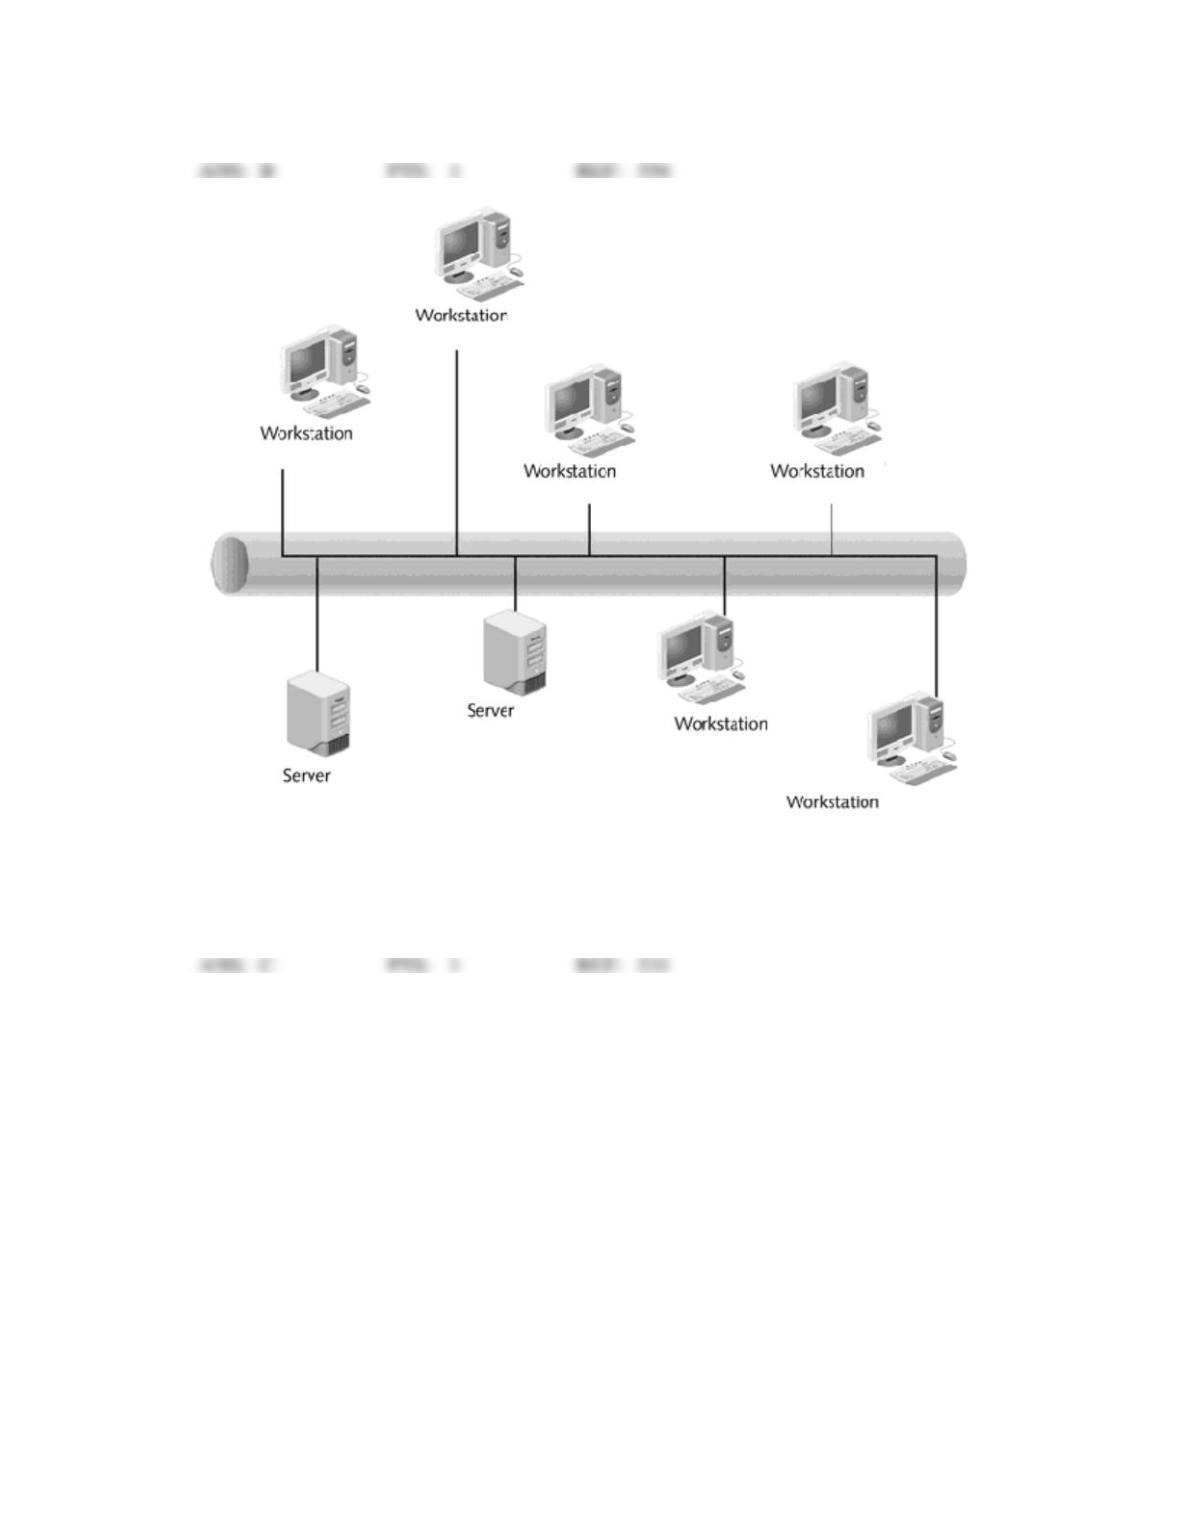
33. If a network administrator wants to use host-based intrusion detection, which devices in the figure
above would need to be configured?
a.
Only the workstations
c.
All workstations and servers
b.
Only the servers
d.
None of the workstations or servers
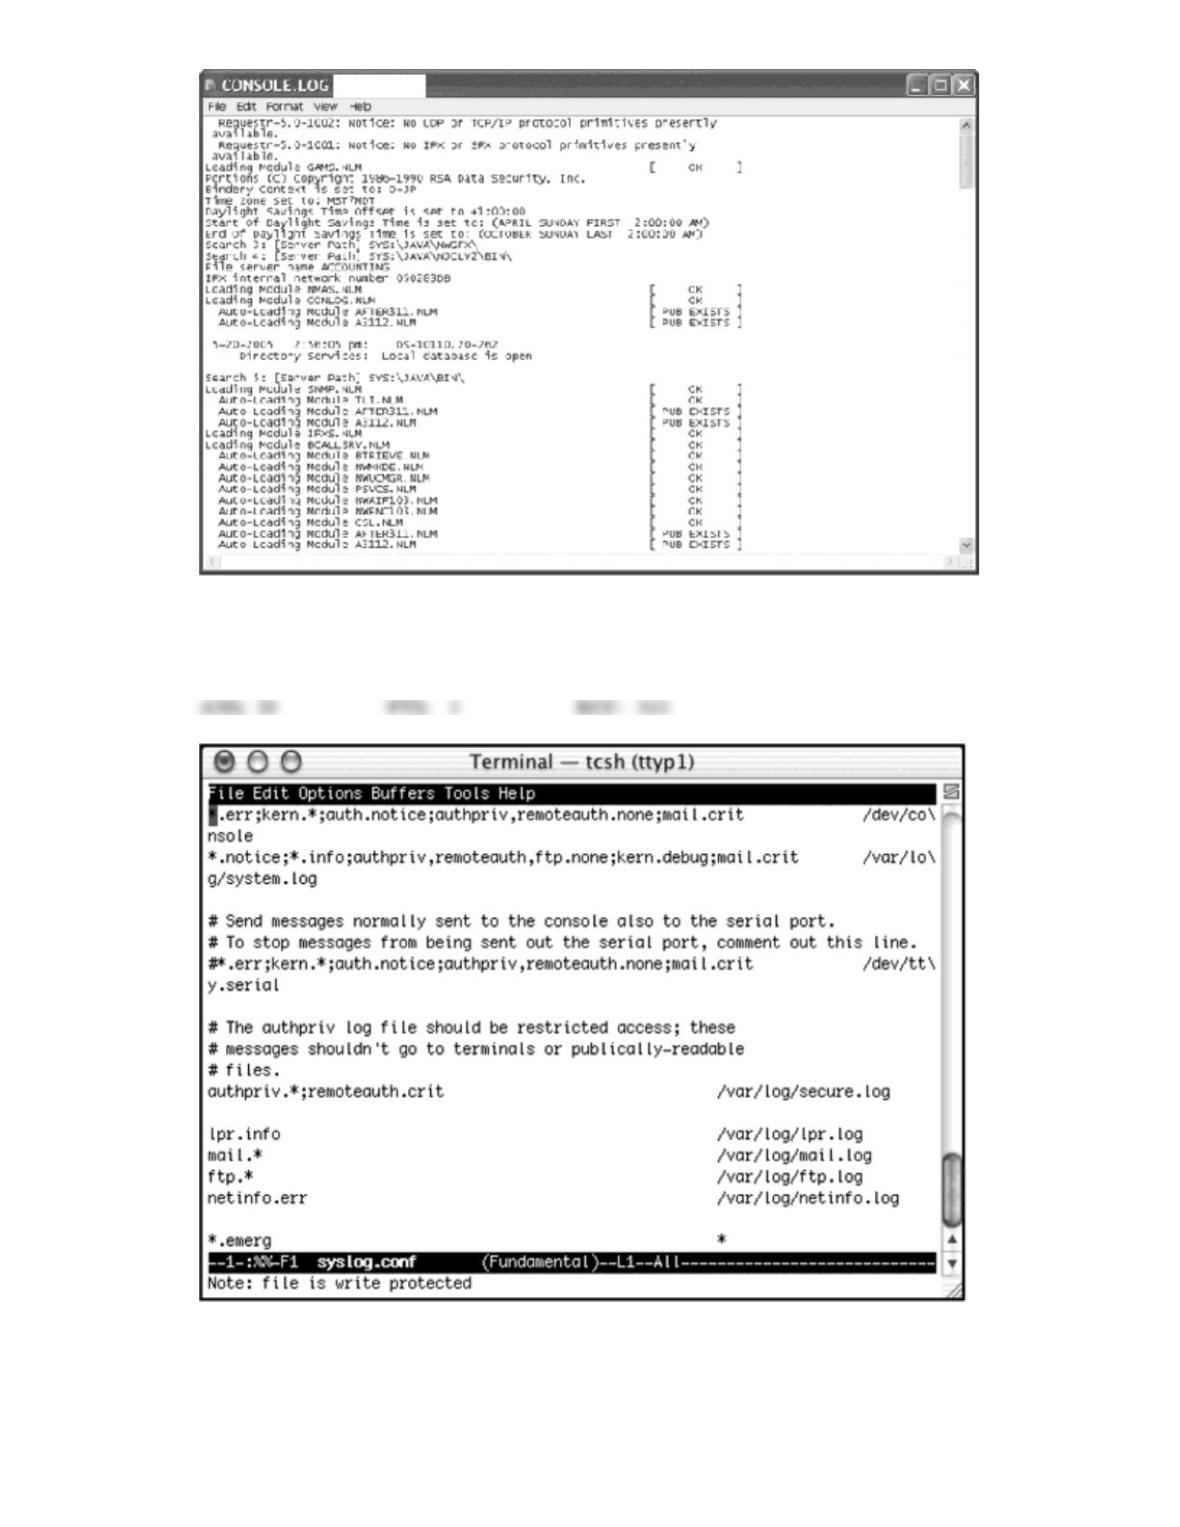
34. Which Netware 6.x log is displayed in the figure above?
a.
Access
c.
Module
b.
Audit
d.
Console
35. Which file is being edited in the figure above?
a.
netinfo log
c.
syslog.conf
b.
lpr.log
d.
system.log
YES/NO
1. Does the Netware 6.x Console log contain error information recorded for the NetWare server?
2. Is the System Log in Mac OS X contained in the file messages.x?
3. Are the Mac OS X logs located in the /var/log directory?
4. Are the Server logs for Mac OS X automatically rotated?
5. In Window Server 2003, does the print$ share enable you to view the number of clients currently using
the server as a print server?
6. Does the Netware Remote Manager allow you to send messages to a particular user or to all users?
7. Is the Process Viewer used by Linux Red Hat 9.x to display a listing of processes and the users who
are running those processes?
8. In Windows 2000 Server, is it necessary to install Network Monitor and Network Monitor Driver
separately?
9. Can the version of Network Monitor that comes with Windows Server 2003 capture and read the
contents of any frames transported on the network segment to which the host computer is connected?
10. Can Network Monitor filter frames and packets on the basis of SAP or ETYPE?
COMPLETION
1. A(n) ____________________ can be acquired by using performance monitoring to establish slow,
average, and peak periods for a network, and keeping records on these periods.
2. At minimum, ____________________ intrusion detection alerts a server or network administrator
about an attack or intrusion, so the administrator can take action.
3. Host wrapper software, which may also be called a(n) ____________________, monitors network
activity into or out of the computer, including protocols, packets, broadcasts, remote logon attempts,
dial-in attempts, port scanning, and other activities.
4. Network-based intrusion-detection software is used on a computer or network device and typically
places the NIC on that device in ____________________ mode.
5. A(n) ____________________ is a command-line string issued remotely that is intended to weaken the
security or to alter an operating system.
6. Typically, an IDS ____________________ is software that automatically records information to a log.
7. In Windows Server 2003, the ____________________ log records information about logon accesses
and file, folder, and system policy changes.
8. In Windows Server 2003, the ____________________ log records information about how software
applications are performing.
9. In Red Hat Linux, the ____________________ Log provides information about jobs that are
scheduled to run or that have already run, such as information about the number of minutes until a
specific job will run.
10. In Red Hat Linux, log files are managed through a process called ____________________.
MATCHING
Match the following terms to the appropriate definition.
a.
Active intrusion detection
f.
Inspector
b.
Alert
g.
IDS
c.
Auditor
h.
Passive intrusion detection
d.
Decoy
i.
Trap
e.
Filter
j.
Trigger
1. Setting up ways to detect and record intrusion attempts, without taking action
2. A message sent to an administrator about a specific operating system event
3. Used to attract attackers
4. Used to detect and report possible network and computer system intrusions
5. Sends an alert to an administrator or takes an action to block an attack
6. Records specific situations that an administrator wants to be warned about
7. Tracks a wide range of data and events related to an operating system
8. Performs a specific function when a predefined situation occurs
9. A viewing capability that enables you to display only specific events
10. Examines captured data and determines if there has been an intrusion
SHORT ANSWER
1. List five third-party passive intrusion-detection tools.
2. List four third-party active intrusion-detection tools.
3. What five activities are typically encompassed by host-based IDS?
4. What five things do inspectors typically look for?
5. List eight different types of information that might be found in a log created by an auditor.
6. What two purposes does a honeypot serve for an organization?
7. In the Windows 2000 Computer Management tool, what three options under Shared Folders provide
information about users currently logged on to the operating system?
8. What two useful tools does NetWare offers to view user connections?
9. List eight server monitoring functions that can be viewed using the Netware MONITOR command.
10. What four tasks can be accomplished using NetWare Remote Manager?